Insights

Analysis from the practice

What we learn running security and compliance programmes — regulation, frameworks and the operational detail that decides whether a programme holds up.

cyber-resilience-act-cra-what-changes-with-etsis-17-draft-standards-in-2026-banner
Frameworks & Compliance11 min read

Cyber Resilience Act (CRA): What Changes with ETSI’s 17 Draft Standards in 2026

The CRA enters its operational phase with 17 ETSI draft standards. DarkProtect analyses timelines, SBOMs, supply chain security and product compliance.

Read article
ot-security-is-not-just-it-security-with-different-devices-banner
Strategy & Leadership4 min read

OT Security Is Not Just IT Security with Different Devices

OT security is not simply IT security applied to different devices. When cyber risk reaches industrial environments, the consequences can affect…

Read article
ai-epistemology-different-llms-better-security-decisions-banner
Strategy & Leadership3 min read

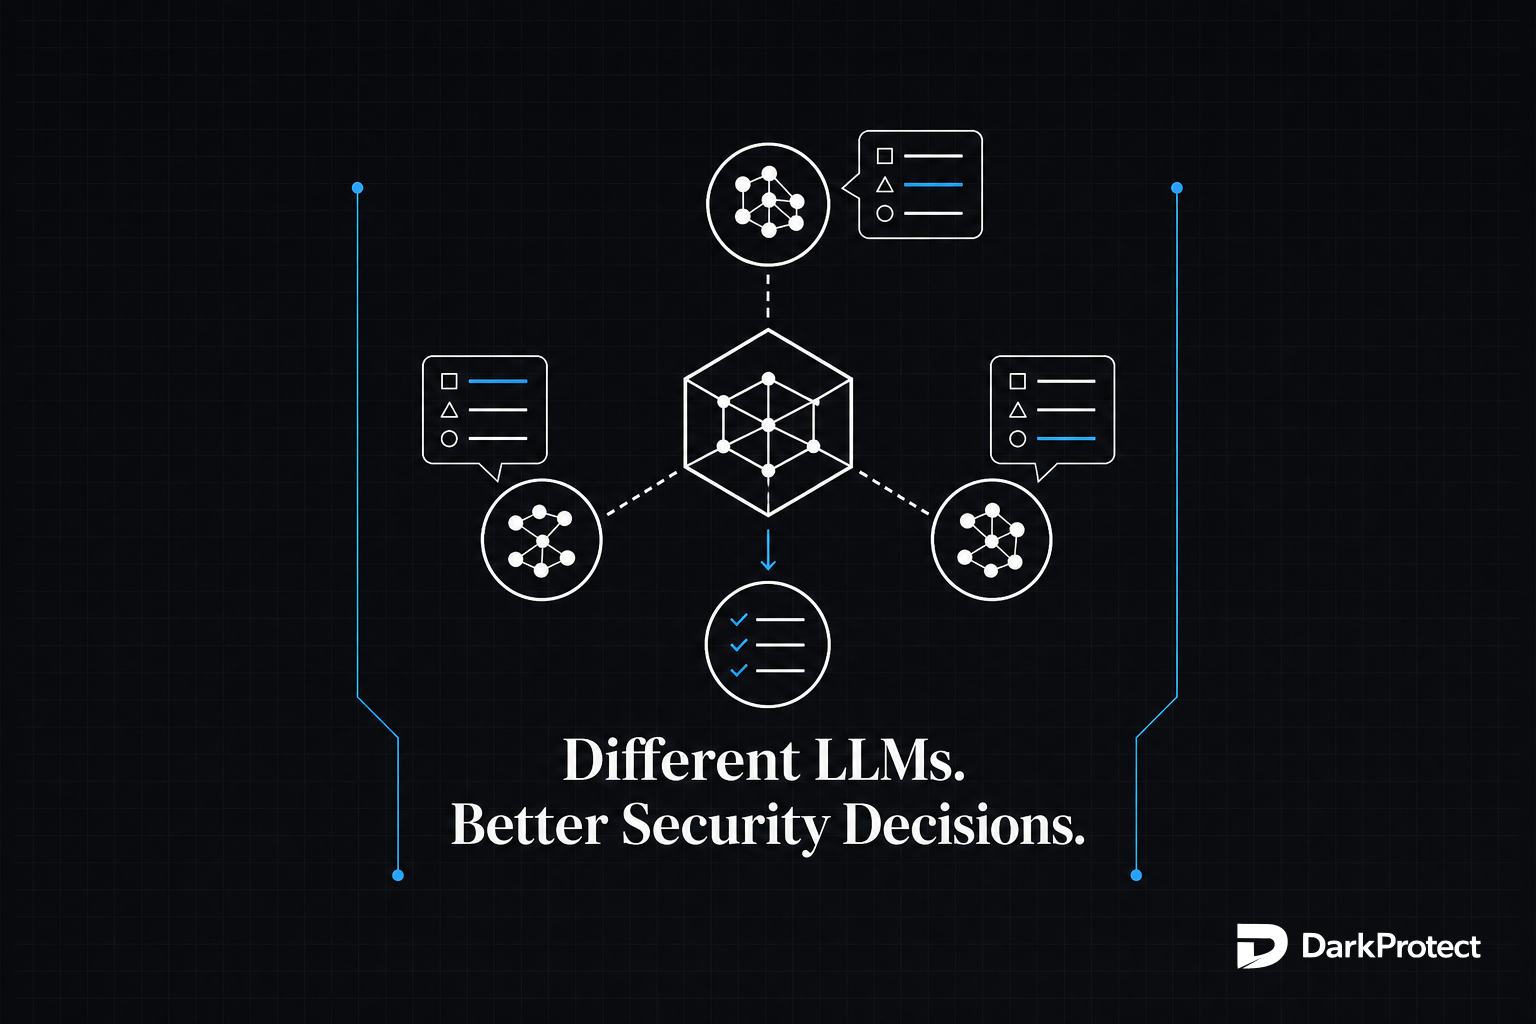
AI Epistemology: Different LLMs, Better Security Decisions

Different LLMs can challenge the same security problem from different perspectives, exposing blind spots and improving the final decision. The future…

Read article

Let's talk about your security program

A free 30-minute conversation, no pitch. We'll map where you stand, the standards you need to meet, and the most direct path to get there.